Brian Harrell is a security and critical infrastructure expert with more than two decades of experience spanning the U.S. Marine Corps, law enforcement, cybersecurity, physical security, and federal government leadership. He previously served as the sixth Assistant Secretary for Infrastructure Protection at the U.S. Department of Homeland Security and as the first Assistant Director for Infrastructure Security at CISA, where he helped lead efforts to protect sectors including energy, water, financial services, communications, and transportation. Today, Harrell advises organizations on preparedness, risk reduction, and response to physical and cyber threats, including through his roles on the Advisory Board of Shooter Detection Systems and the Security Industry Association’s Board of Directors. Pulse 2.0 interviewed Brian Harrell to learn more about physical security risk, critical infrastructure protection, security convergence, and real-time threat detection. Pulse 2.0 interviewed Brian Harrell to learn more.
Brian Harrell’s Background
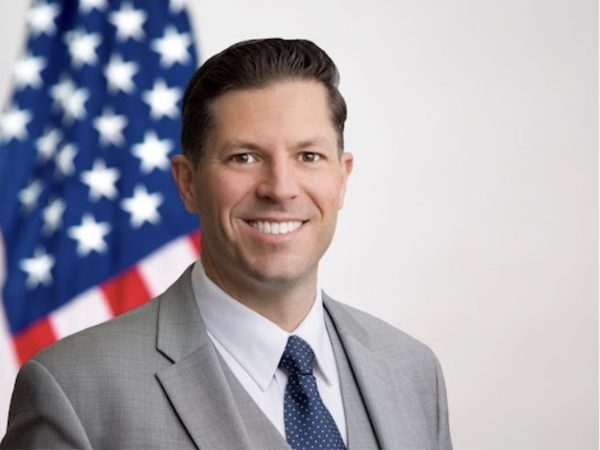
When asked about his background, Harrell shared:
I’ve spent more than two decades working to protect public and private sector assets from physical and cyber threats. I began my career serving in the U.S. Marine Corps and as a law enforcement officer in Los Angeles, two experiences that shaped my operational approach to security and crisis response.
From there I moved into the critical infrastructure space, holding leadership roles at the North American Electric Reliability Corporation, where I worked to strengthen protections for North America’s electric grid against both physical and cyber threats.
In 2018, I was appointed by the President to serve as the sixth Assistant Secretary for Infrastructure Protection at the U.S. Department of Homeland Security. In that role, I led national efforts to safeguard the country’s most vital sectors, including energy, water, financial services, communications, and transportation, working closely with government and private sector partners to strengthen the security and resilience of U.S. critical infrastructure.
During my tenure, I also served as the first Assistant Director for Infrastructure Security at CISA, where I helped establish and lead the agency’s infrastructure protection mission.
Today, I serve on the Advisory Board for Shooter Detection Systems, a leader in real-time gunshot detection technology, as well as the Security Industry Association’s Board of Directors, where I advise organizations on strategies to strengthen preparedness, reduce risk, and improve response to active threats and other security incidents.
Physical Security As Enterprise Risk
When asked how boards should think about physical security as a distinct category of enterprise risk and where gaps typically exist in board-level oversight, Harrell explained:
Boards have made enormous strides in elevating cyber risk to a board-level conversation, and physical security deserves the same seat at the table. The reality is that an active shooter event, an attack on a facility, or a targeted strike on a corporate leader can be just as financially and operationally devastating as a major data breach. Yet in most boardrooms, physical security still gets treated as a facilities or HR issue rather than a strategic risk category.
Most organizations today have invested heavily in front-end protections such as surveillance, access control, and screening. These are essential, but they rely on the assumption that a threat will be identified before an incident occurs. That assumption does not always hold. Similar to my ongoing cyber strategy, prevention is important, but equally critical is detection and response.
As a result, organizations are increasingly focusing on adding an additional layer centered on real-time detection. Technologies that provide immediate, verified awareness the moment an incident begins allow security teams and first responders to act faster and with greater accuracy.
When safety and security appear on board agendas, the Chief Security Officer (CSO) must be prepared to clearly articulate the risk landscape, the technology options, and how layered security approaches can reduce exposure and improve outcomes.
Convergence Of Cyber And Physical Threats
When asked how Chief Security Officers are advising leadership as tensions with Iran escalate and what a coordinated cyber and physical response framework looks like, Harrell noted:
CSOs are increasingly advising leadership to view cyber and physical threats as interconnected rather than separate risk domains. Today’s threat landscape is deeply blended. Disruptions that begin in one domain can quickly cascade into the other, whether through infrastructure targeting, supply chain disruption, or coordinated attacks.
In practice, an effective response requires a unified framework with shared visibility, aligned communication channels, and clearly defined roles across teams. The most prepared organizations have integrated their threat intelligence, response protocols, and communication systems, enabling them to act quickly and cohesively under pressure.
This also means ensuring that both cyber and physical incidents can be detected and communicated in real time, allowing leadership to make informed decisions as situations evolve.
At the same time, while Iran’s domestic infrastructure may currently be constrained, its proxy networks remain active. Other nation-state actors, including China, North Korea, and Russia, continue to look for opportunities to exploit vulnerabilities. As Iran regains capability, retaliation from IRGC-affiliated actors remains a credible risk. In this environment, security teams should be preparing for potential attacks on critical infrastructure, including industrial control systems (ICS).
Duty Of Care And Liability
When asked about companies’ duty-of-care obligations when a physical threat occurs on or near corporate property and how the liability landscape is changing, Harrell said:
Boards no longer have the luxury of inaction when credible protective technologies already exist. After a violent incident, a predictable process follows, including legal reviews, internal audits, and regulatory scrutiny. Across all of those reviews, the same questions arise: What did you know, when did you know it, and what did you do about it?
Increasingly, organizations are being evaluated not just against industry norms, but against what is technologically possible. If a company lacked real-time detection capabilities when solutions were widely available, that gap can become a focal point in assessing due diligence and liability.
This shift is pushing organizations to adopt technologies that provide faster, more reliable situational awareness during an incident, helping demonstrate a proactive approach to risk management.
Elevating Security To The Board Level
When asked what patterns he observed at DHS and CISA around enterprises underinvesting in physical threat preparedness relative to cybersecurity, Harrell explained:
Most mature organizations have fully embraced “convergence,” bringing cybersecurity and physical security together under a single leader, often the Chief Security Officer. This approach drives greater efficiency, visibility, and intelligence sharing across the broader security risk landscape. Building an organization that removes silos is the first step.
At the same time, corporate boards are increasingly seeking regular threat briefings and deeper discussions around security investments and risk mitigation. Major events, whether cyber breaches, wildfires, or incidents of workplace violence, inevitably require board-level engagement. Now is the time to proactively involve them, walking through response scenarios and expectations.
Boards will want to understand how the company plans to engage regulators, manage communications across social media, interact with elected officials, and, of course, support customers. Establishing this “muscle memory” through structured exercises is critical.
While the board’s role is not operational, it plays a vital part in providing strategic guidance on complex, high-stakes challenges.
Business Continuity And Threat Scenarios
When asked how security leaders should model coordinated attacks on infrastructure and targeted violence in business continuity planning, Harrell noted:
Active shooter events are among the most financially disruptive scenarios an organization can face, not only because of potential loss of life, but because of the cascading operational consequences. Facilities shut down, employees are displaced, customers lose confidence, and productivity can stall for extended periods.
One of the most overlooked dependencies is time to clarity. The longer it takes to understand what happened, where it occurred, and whether the threat is ongoing, the longer it takes to stabilize operations.
Real-time detection capabilities can play a critical role here by providing immediate, verified awareness from the first moment of an incident. This allows security teams and first responders to coordinate more effectively and can help accelerate both response and recovery timelines.
Evaluating Prevention And Detection Technology
When asked what role prevention technology should play in enterprise physical security strategy and how organizations can distinguish tools that reduce risk from those that provide a false sense of protection, Harrell explained:
A significant percentage of gun violence in corporate environments involves insiders or former employees who understand security processes and know how to bypass controls.
This is why prevention alone is not sufficient. While access control, surveillance, and screening are critical, they are not foolproof.
A layered approach is essential, and real-time detection plays a key role in that strategy. For example, Shooter Detection Systems’ technology approach uses multi-mode acoustic and infrared sensors combined with edge-based processing to detect and verify gunfire in real time, automatically generating a validated alert without requiring human confirmation.
When you have immediate, precise intelligence on board, it allows security teams to understand where an incident is occurring and how it is progressing. By integrating with existing security systems, it enables faster and more coordinated responses.
When evaluating technologies, organizations should focus on whether a solution reduces response time and improves decision-making under pressure, rather than relying on systems that depend on delayed interpretation.
Integrating Physical And Cyber Intelligence
When asked how sophisticated organizations are integrating physical and cyber threat intelligence into a unified risk picture, Harrell said:
The most sophisticated organizations are moving toward unified risk models where physical and cyber threats are assessed together. This requires alignment across teams, shared data, and integrated systems that provide a comprehensive view of risk.
Real-time detection technologies play an important role in this by feeding actionable data into broader security ecosystems, improving visibility and coordination across the organization.
The First 90 Days
When asked what companies just beginning to elevate security to the board agenda should prioritize during their first 90 days, Harrell outlined three areas:
When safety and security appear on board agendas, leadership must focus on defining risk exposure, identifying the right technologies, and aligning stakeholders around investment decisions.
First, organizations should identify their highest-risk areas, particularly high-traffic and publicly accessible spaces such as lobbies and shared environments.
Second, they should begin implementing a layered approach that includes real-time detection capabilities. Technologies like SDS allow organizations to start in priority areas and expand over time, providing immediate awareness and helping reduce exposure quickly.
Third, leadership must address common concerns around cost, probability, and privacy. It is important to clarify that modern detection technologies are purpose-built for emergency response and do not record conversations or monitor behavior. Their role is to provide accurate, real-time information so responders can act quickly and effectively.
Connecting Detection And Response
When invited to discuss another topic, Harrell concluded:
One area I think deserves more attention is the technology layer that sits between detection and response, and it’s an area where I’ve spent a lot of time in my advisory role at SDS.
SDS uses multi-mode acoustic and infrared sensors combined with edge-based processing to detect, verify, and identify gunfire, automatically generating a validated alert that does not require manual confirmation. That last part matters; removing reliance on human intervention during high-stress situations is critical when seconds count.
The system integrates with more than 50 leading security platforms, including video surveillance, access control, and mass notification systems, enabling automated responses such as lockdowns and activation of emergency protocols.
It also does not record conversations or compromise sensitive data, which addresses one of the most common concerns I hear from leadership teams when this technology comes up.
For organizations evaluating their options, it’s worth noting that SDS is the only manufacturer whose indoor gunshot detection system holds the highest level of U.S. Department of Homeland Security SAFETY Act Certification.