As Executive Vice President, GRC Solutions Strategy at Mitratech, Jan Stappers leads key strategic initiatives and is a recognized expert in whistleblowing management, data privacy, and regulatory compliance. He contributed to ISO 37002, is CIPP/E certified, serves on the UNECE Working Party on Regulatory Cooperation and Standardization Policies, and helps organizations navigate increasingly complex governance, risk, and compliance requirements. Pulse 2.0 interviewed Mitratech’s Jan Stappers to learn more about his perspective.
Jan Stappers’ Background
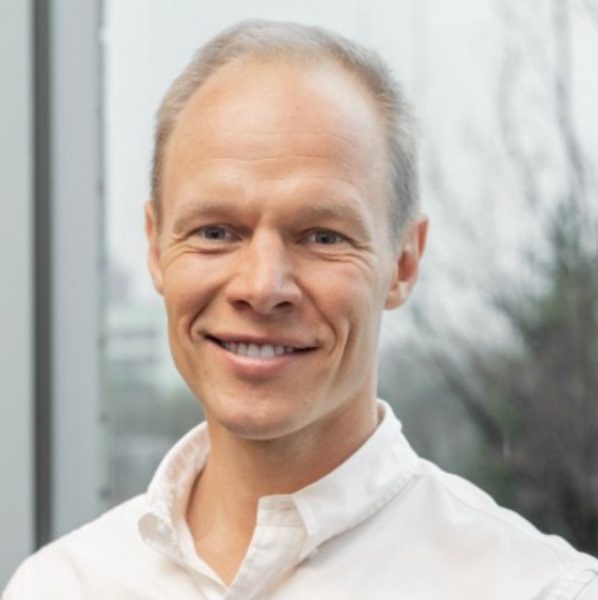
When asked what drew him to regulatory law and applied GRC practice and how his career has shaped his view of good governance, Stappers shared:
I did not set out to work in compliance. I started with a genuine interest in the relationship between law and organizational behavior, specifically the question of why organizations follow rules, and when and why they do not. When I paired that with developments in legal tech, it turned out to be a career in itself.
The academic grounding at Leiden and King’s College gave me a way of reading regulatory frameworks critically rather than just descriptively. When you are trained in law, you learn to look past the text of a rule to what it is actually trying to achieve. That matters enormously in GRC, where organizations frequently comply with the letter of a requirement while missing its purpose entirely.
My time contributing to the UNECE working group on risk management in regulatory systems, and the work I did around ISO 37002 on whistleblowing management systems, reinforced something I now hold as a core conviction: the most important governance questions are not technical questions. They are questions about culture, about accountability, and about whether the people inside an organization feel safe enough to tell the truth. Technology can support that. It cannot replace it.
What good governance actually looks like in practice is organizations where compliance is not a department you call when something goes wrong. It is a normal part of how decisions get made. The organizations I have seen get this right tend to share one characteristic: leadership that genuinely wants to know when something is not working. That sounds simple, but it is surprisingly rare.
GRC Solutions Strategy
When asked about his responsibilities in GRC Solutions Strategy at Mitratech and how the embedded advisory model differs from a traditional vendor relationship, Stappers explained:
My role sits at the intersection of regulatory intelligence, customer strategy, and go-to-market thinking. In practical terms, that means working directly with customers and prospects on the regulatory challenges they are navigating, helping translate complex and often overlapping compliance obligations into program decisions they can actually act on, and advising on where the platform adds the most value relative to their specific risk profile, while empowering my colleagues throughout the organization to facilitate the same.
The difference between an embedded advisory model and a traditional vendor relationship comes down to the question you start with. A traditional vendor relationship typically starts from the product with: here is what we have and here is how it maps to your requirements. An advisory model starts from the organization’s situation. The perspective considers what you are facing, what good looks like, and where technology can close the gap between the two.
That distinction matters because most compliance programs fail not for lack of technology but for lack of clarity about what problem is being solved. Organizations in heavily regulated sectors are dealing with a dozen overlapping frameworks simultaneously, each requiring slightly different things, with different enforcement timelines and different consequences for failure.
An advisory model helps them build a coherent program rather than assemble a collection of point solutions that each pass a different test but do not add up to a defensible whole.
What we are building at Mitratech is the capacity to have that conversation at a genuinely senior level, with the depth that CCOs, general counsel, and CROs need to make confident program decisions. That is the value of embedding advisory expertise inside the platform relationship, rather than treating it as a separate professional services engagement.
Why Practitioner-Led Guidance Matters
When asked about a defining moment since joining Mitratech that reinforced why practitioner-led guidance matters, Stappers said:
I joined Mitratech in February 2026, and then six weeks later we launched the Global GRC Platform. A few weeks after the launch, I was on a call with a large US retailer. They had a third-party risk platform, an enterprise risk management system, and a policy management tool. On paper, a well-equipped compliance function.
About twenty minutes in, the head of vendor risk said something that has stayed with me. When I asked whether he had a clear view of how his program connected to the rest of the organization’s compliance posture, he said: “We’re not privy to a lot of what goes on with the other areas of the enterprise. I couldn’t tell you whether there are any gaps between us.”
This was not a person who lacked experience or seniority. He was articulate, thoughtful, and clearly doing his job well. But the tools his organization had invested in existed in organizational silos that nobody had ever been asked to bridge. The data moved from one environment to the other by manual export. Nobody had a connected view.
That moment reinforced the core premise of the advisory model. The gap between compliance program intent and compliance program reality is almost always an integration problem, not a capability problem.
Organizations rarely fail because they lack the right tools. They fail because those tools have never been assembled into a program that a regulator, a board, or an auditor can actually interrogate as a whole. That is the conversation practitioner-led guidance is designed to start.
The Global GRC Platform
When asked what it means for organizations to connect more than 11 GRC domains through a single intelligence layer rather than managing point solutions, Stappers explained:
The compliance challenge most organizations are dealing with right now is not a lack of tools. It is a lack of connection between tools. They have a hotline here, a vendor risk system there, a policy management platform somewhere else, and none of them are talking to each other.
The result is that nobody has a complete picture of the organization’s compliance position, and when something goes wrong, the gaps are exactly where the joins were.
A single intelligence layer changes that in a fundamental way. When whistleblowing data connects to your third-party risk program, you start to see patterns that are invisible when those systems are separate.
When your policy management platform connects to your training records, you can evidence not just that policies exist but that people have read them, understood them, and attested to them.
When your enterprise risk framework maps directly to a live regulatory content library, you can see which of your controls are covering which obligations, and where the white space is.
The launch of the Global GRC Platform on 30 March 2026 represented Mitratech doing something that most of our competitors have not yet managed: connecting all of that in a way that is genuinely integrated rather than just co-branded.
The ARIES™ AI layer is part of that story, but the more important part is the underlying data architecture. AI can only produce useful insights if it is working across connected, structured data. The platform is the foundation that makes the intelligence possible.
From an advisory perspective, the practical implication is significant. It means we can have a conversation with a CCO about their entire compliance program, not just the product they are currently using.
And it means that when we identify a gap, the path to addressing it is a program extension rather than a procurement process.
Regulatory Pressure Across EMEA And APAC
When asked about the compliance challenges organizations are struggling with most as regulatory pressure intensifies across EMEA and APAC, Stappers said:
The honest answer is that the challenge is not any single regulation. It is the simultaneous arrival of multiple significant frameworks, each of which individually would represent a serious compliance project, all landing at roughly the same time.
In EMEA, the organizations I am talking to right now are managing the full enforcement of the EU AI Act from December 2027, the publication of the EU Anti-Corruption Directive in May 2026 with transposition timelines running to the end of 2028, ECCTA agency mobilization in the UK, which accelerated significantly this year, and the ongoing practical implementation of DORA and NIS2 for financial and critical infrastructure organizations.
These are not incremental adjustments to existing programs. Several of them require building new capabilities from scratch.
In APAC, the pattern is similar but less uniform. Australia, Singapore, and Japan are each at different stages of developing whistleblower protection frameworks and third-party risk requirements, and the cross-border complexity for multinationals operating across all three is significant.
The challenge I see most consistently is the gap between regulatory awareness and program action. Organizations know these frameworks are coming. Many have done the initial mapping work.
Where they get stuck is in translating that awareness into a defensible, operational program that they can evidence to a regulator or auditor.
That last step, building the audit trail, connecting the training records, getting the policies into the hands of every employee across every jurisdiction, is where most organizations are still relying on spreadsheets and manual processes. That is exactly the gap that integrated GRC technology is designed to close.
The organizations responding most effectively are the ones treating this as a moment to build a lasting program infrastructure rather than to pass the immediate compliance test.
The ones who built strong GDPR programs in 2018 found that the investment paid dividends across every subsequent privacy and data regulation. The same logic applies here.
Whistleblowing And Speak-Up Culture
When asked how whistleblowing and internal reporting culture have evolved and what a genuine speak-up culture looks like, Stappers explained:
The whistleblowing space has changed considerably in the roughly nine years I have been working seriously in it. The early conversation was almost entirely about mechanics: do you have a hotline? Does it take anonymous reports? Is it available in the right languages? Those are still important questions, but they are table stakes now. The conversation has moved on.
The more substantive shift has been regulatory. The EU Whistleblower Directive, transposed across Member States over the last few years, established baseline requirements that many organizations had not previously met.
ISO 37002, the international whistleblowing management systems guidance, gave organizations a framework for thinking about internal reporting as a system to be managed rather than a box to be checked.
The EU Anti-Corruption Directive, adopted this year, creates additional obligations around confidential reporting channels that will require program review from organizations across the EU and those with significant EU operations.
But the most important shift has been cultural, and it is the one that technology cannot fully address. Genuine speak-up culture is not a function of having the right system in place. It is a function of what happens after someone uses it.
Employees are rational actors. They watch what happens to the people who report. If concerns are investigated promptly, handled fairly, and followed up on, reporting rates increase. If concerns disappear into a process and nothing visible changes, reporting rates fall regardless of how accessible the channel is.
What does it look like when it is working? It produces reporting rates that reflect the actual level of ethical risk in the organization, a spread of report types that goes beyond the most serious incidents to include the early signals, a senior leadership team that treats the data from the hotline as a meaningful indicator of organizational health rather than a compliance metric to be managed, and an investigation process that resolves cases within reasonable timeframes with clear outcomes.
That is the standard. Most organizations are some distance from it. The ones who invest in getting there find that it changes the relationship between the compliance function and the rest of the business.
Responsible AI Deployment
When asked what responsible AI deployment requires from organizations, particularly in GRC, Stappers said:
I should start by acknowledging the obvious tension in this question. We are a GRC company with an AI product making the case for responsible AI governance. I want to be honest about that rather than pretend the question is straightforward.
ARIES™ is built on a set of principles that I think are genuinely important: Customer data is never used to train AI models, the system shows its reasoning rather than producing outputs that cannot be interrogated, and decisions remain with the human expert rather than being delegated to the AI.
Those are not just design choices. They are a position on what AI should be doing in high-stakes compliance contexts.
For organizations considering their own AI deployment, the EU AI Act provides a useful framework, and while the high-risk AI obligations were pushed to December 2027 under the AI Omnibus agreed in May 2026, that deferral should not be read as a signal to wait.
The documentation, human oversight, and monitoring requirements that apply to high-risk AI systems take time to build properly. Organizations that use this additional time well will be in a materially stronger position than those that treat it as a reprieve.
The most important question is not “what can this AI do?” but “what is this AI optimizing for, and how would I know if it got it wrong?”
AI systems in GRC contexts are often working with inherently ambiguous data: qualitative risk assessments, sentiment signals from reporting channels, third-party vendor responses to questionnaires.
The risk of AI in these contexts is not that it will produce obviously wrong answers. It is that it will produce plausible-sounding answers that embed assumptions the organization has not interrogated.
Responsible deployment requires three things that go beyond technical compliance with the AI Act: a clear statement of what the AI is and is not expected to decide, a human review process with genuine authority to override AI outputs, and an audit trail that makes the AI’s contribution to any consequential decision visible and reviewable.
The third element is often missing. It is essential.
Key Milestones And Regulatory Shifts
When asked about milestones, regulatory shifts, platform capabilities, and customer outcomes that have stood out since he joined Mitratech, Stappers highlighted:
The Global GRC Platform launch in March 2026 was significant, not just as a product milestone but as a signal about where the market is heading.
The response from compliance leaders and from the analyst community confirmed something I had been hearing consistently in customer conversations: organizations want a connected program, not a collection of discrete tools, and they have been waiting for a vendor to deliver it in a way that is genuinely integrated rather than just bundled.
The adoption of the EU Anti-Corruption Directive during the same period was a remarkable coincidence of timing. The European Parliament adopted its position on the directive the same week as our platform launch; the Council completed formal adoption on 21 April 2026.
The timing was striking: the platform that addresses the directive’s core program requirements went live in the same week that the legislative process concluded in Parliament.
Conversations with customers about the ACD have changed since then because the buying window is now real. Program build takes 12 to 24 months. Organizations that start now will be in a defensible position when Member State transposition deadlines arrive around 2028. Those who wait will be reacting.
The ARIES™ AI rollout across the platform has also been a milestone worth noting.
Seeing customers use AI to accelerate their risk assessments and mitigation planning, while maintaining the audit trail and human review that their regulators require, is a reasonable early indicator of what responsible AI deployment looks like in practice.
Customer Outcomes
When asked about the types of organizations Mitratech serves and the outcomes they are achieving through the combination of platform and advisory capabilities, Stappers explained:
Mitratech serves organizations across the full size and sector spectrum, from mid-market companies navigating their first serious compliance program to large multinationals managing regulatory obligations across dozens of jurisdictions simultaneously.
The Global GRC platform specifically tends to be most relevant for organizations where the compliance function has moved beyond basic box-ticking and is being asked to demonstrate program maturity to regulators, boards, and auditors.
In financial services, the DORA and NIS2 implementation conversations have been consistent: organizations that had previously managed ICT third-party risk through annual assessments are realizing that point-in-time evaluation is no longer what regulators expect, and they are building continuous monitoring capabilities.
In the broader corporate sector, the ECCTA and EU ACD conversations are bringing anti-corruption program requirements into scope for organizations that had previously treated them as a US or UK-only concern.
The outcomes that come up consistently in customer conversations tend to cluster around three things.
First, evidence quality: the ability to demonstrate to a regulator or auditor not just that controls exist but that they are operating effectively, with a connected audit trail across training, policy acknowledgement, and incident reporting.
Second, efficiency: replacing manual assembly of board compliance reports with automated views that can be produced on demand rather than over several days of consolidation work.
Third, confidence: the shift from a compliance team that is always slightly behind the regulatory curve to one that can see what is coming and plan ahead.
The advisory component specifically tends to add value at the moments when the regulatory picture is changing faster than the organization’s internal capacity to interpret it. That is precisely the moment we are in across EMEA and APAC right now.
The Future Of The GRC Market
When asked where the GRC market is heading over the next two to three years, Stappers said:
The direction is reasonably clear, even if the pace is not. GRC is moving from a compliance function, focused on passing regulatory tests, to a risk intelligence function, focused on giving leadership the information they need to make better decisions.
The regulatory pressure driving that shift is not going to ease. If anything, the simultaneous arrival of the EU AI Act, the EU Anti-Corruption Directive, ongoing DORA and NIS2 implementation, and the UK’s ECCTA enforcement signals that the next two to three years will be among the most demanding compliance periods most organizations have experienced.
In terms of market structure, the current fragmentation of the technology landscape cannot persist.
Organizations are increasingly unwilling to manage seven or eight separate compliance platforms, each requiring its own integration, data governance, and stakeholder relationships.
The consolidation pressure is real, and it will continue to favor vendors who can offer genuine breadth with genuine depth, not just a product catalog.
What separates the organizations that will navigate this well from those that will not is less about resources than it might appear.
The organizations I see handling regulatory complexity most effectively tend to share a common characteristic: they invest in program infrastructure before they are forced to.
They do not wait for an enforcement action or a supervisory examination to build a defensible audit trail. They treat compliance as a strategic capability that gives the business greater freedom to operate, rather than a cost center that exists to prevent bad things from happening.
The practical implication for technology decisions is significant. Organizations that are choosing their GRC platform now are making a decision that will shape their compliance infrastructure for the next five to ten years.
The question worth asking is not just “does this solve our current problem?” but “does this give us the foundation to address the problems we have not seen yet?”
The regulatory landscape in 2028 will look materially different from the one we are managing today. The organizations that built on a connected platform rather than a collection of point solutions will be in a far stronger position to respond and succeed.
The GRC Market Opportunity
When invited to share another perspective with technology leaders, investors, and enterprise decision-makers, Stappers concluded:
One observation I would leave with a technology-focused audience is this: the GRC market is one of the few areas of enterprise software where the gap between market need and market sophistication is still genuinely large.
Most large organizations have significant compliance obligations and genuinely inadequate infrastructure for managing them. That combination of regulatory pressure, technology lag, and rising stakes creates a market dynamic that is not going away.
For investors, the key signal to watch is not headline regulatory deadlines but enforcement behavior. Regulators across the EU and UK have been explicit in recent years that they intend to use penalties as a lever for behavior change, not just as a response to egregious violations.
The organizations that respond to that signal by building structural compliance capabilities will differentiate themselves. The ones who continue to treat compliance as a reactive function will find the cost of inaction rising faster than they expect.
For enterprise decision-makers specifically: the conversation about compliance technology has changed. It is no longer a question of whether you need it.
It is a question of whether you are building on a foundation that is integrated enough to give you a defensible, evidenceable program, or whether you are assembling a set of tools that will each pass a different test but will not produce a coherent picture of your compliance position.
That second scenario is increasingly the one that draws regulatory attention.
The GRC market is entering a period of genuine maturity. The organizations and vendors that understand what that means will build something lasting. The ones that do not will find themselves managing the consequences of decisions made in an earlier, simpler moment.