TechRiot.io is a cybersecurity media, research, education, and advisory organization focused on helping security professionals understand emerging threats and develop practical approaches to securing cloud infrastructure and artificial intelligence systems. Pulse 2.0 interviewed TechRiot.io Co-Founder and CISO Ashish Rajan to learn more about his cybersecurity background, the company’s research initiatives, his book AI Security Engineering, the challenges of securing autonomous AI agents, and the future of enterprise AI security.
Ashish Rajan’s Background
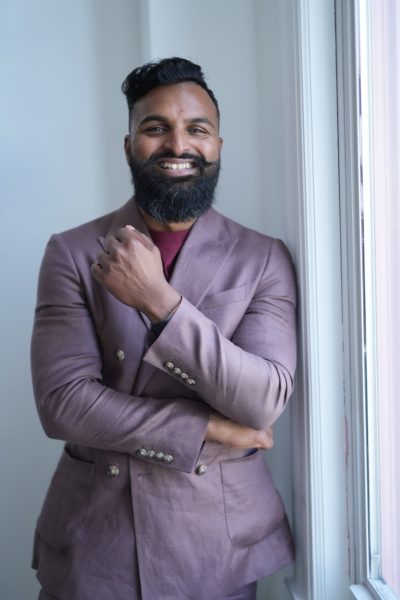
When asked about his professional background and how he became involved in cybersecurity, Rajan shared:
My interest in cybersecurity started when my personal email account was hacked. I wanted to understand how something like that could happen and how to prevent it. That curiosity eventually turned into a career spanning more than 17 years.
I’ve worked across identity, cloud security, security architecture and leadership, including serving as CISO of a global technology company. I’ve also taught security through SANS and spoken at conferences including RSA Conference and Black Hat.
Today, I’m Co-Founder and CISO of TechRiot.io, author of AI Security Engineering (Wiley), Chief Researcher at AI Security Lab, and host of the Cloud Security Podcast and AI Security Podcast.
My focus is increasingly on how organizations build, deploy and secure AI systems, particularly as AI moves beyond answering questions and starts taking actions.
Primary Responsibilities At TechRiot.io
Discussing his responsibilities across cybersecurity research, education, and industry engagement, Rajan outlined:
My work sits at the intersection of cybersecurity research, education and industry engagement.
At TechRiot.io, I focus on our strategic and technical direction, working with security leaders and practitioners across Fortune 500 and Global 2000 organizations, and identifying emerging security challenges that deserve deeper investigation.
Through AI Security Lab, I approach research from a practitioner’s perspective. That means understanding how AI systems and agents are actually deployed in enterprises, what new AI models mean for enterprise security, where traditional controls fall short, and how we can independently verify that security measures work.
A significant part of my time also goes into speaking with practitioners, conducting workshops, writing and sharing what we’re learning with the wider security community.
Core Products And Features
When asked about TechRiot.io’s core offerings, Rajan highlighted the organization’s combination of cybersecurity media, community engagement, education, and independent research:
TechRiot.io brings together cybersecurity media, community, education, research and strategic advisory work.
Our Cloud Security Podcast and AI Security Podcast provide a platform for practitioners and technology leaders to share what they’re learning. We also work with organizations through workshops and advisory engagements.
AI Security Lab is our independent research initiative focused on understanding how AI systems are built, where they fail and how they can be secured.
For example, we’re examining how AI coding agents are configured, what access they have, and whether the security boundaries organizations expect are actually enforced.
We’re translating that work into practical experiments, open-source tools, security checklists and hands-on education.
The idea is to help security professionals move beyond understanding AI risks to being able to investigate and address them themselves.
About The Book AI Security Engineering
When asked about his book AI Security Engineering, Rajan described its focus on applying established cybersecurity principles to emerging artificial intelligence technologies:
AI Security Engineering applies established security engineering principles to the new world of AI systems.
Industry today has a lot of the conversation around AI security focusing on models, prompt injection or governance frameworks. Those are important, but organizations also need to understand the complete systems they’re building: the applications, agents, identities, permissions, tools, data and infrastructure surrounding the models.
The book approaches AI security from an engineering perspective. How do you understand the system you’re building? Where are its trust boundaries? What can go wrong? And how do you design and implement security controls that actually work?
It’s intended to help practitioners move beyond discussing AI risks toward securing real AI applications and systems.
The Inspiration Behind AI Security Engineering
Reflecting on what motivated him to write the book, Rajan pointed to conversations with enterprise security leaders and the growing challenges associated with autonomous AI systems:
Through my work at TechRiot and conversations on AI Security Podcast with security leaders from Visa, Anthropic, DoorDash, Goldman, Bank of America and many more, I started noticing how quickly organizations were adopting AI while security teams were still working out how to secure it.
Many of the challenges weren’t entirely new. We already understood concepts such as least privilege, identity, supply chain security, secure development and monitoring. But applying those principles to AI applications and autonomous agents introduced new questions.
For example, what happens when an AI agent can execute code, access sensitive data or make decisions without someone approving every action? Who would be responsible? Can we re-create what an agent or LLM action did?
I wanted to bring the conversation back to security engineering fundamentals based on what I saw work in Fortune 500 and Global 2000 companies and explore how those principles need to evolve for AI systems.
Key Takeaways From AI Security Engineering
When asked about the book’s most important lessons, Rajan emphasized the importance of securing the entire AI application rather than focusing exclusively on its underlying model:
One of the biggest takeaways is that AI security isn’t just about securing the model.
An AI application is a complete system, and its security depends on everything surrounding the model, including the tools it can use, the data it can access and the actions it’s authorized to perform.
Another important takeaway is that security controls need to be verified. Having a policy or configuration doesn’t automatically mean a system behaves as intended.
As AI systems become more autonomous, understanding what they’re allowed to do, observing what they actually do and independently verifying the outcomes becomes increasingly important.
Challenges In Enterprise AI Security
Addressing the challenges organizations face when securing increasingly capable AI systems, Rajan underscored the need for greater visibility, auditability, and continuous security verification:
One of the biggest challenges I see is that organizations are being asked to secure AI systems without sufficient visibility, auditability or accountability for the actions those systems take.
Security teams are trying to establish which AI applications and agents are being used, what access they have and how they’re interacting with existing enterprise systems.
Meanwhile, frontier AI models continue to advance rapidly. Capabilities that required specialist expertise or significant resources just a few months ago are becoming accessible to a much wider audience. This is accelerating vulnerability discovery and lowering the barrier to identifying and exploiting weaknesses in existing systems.
For enterprises, this creates a difficult reality: security assumptions that were reasonable six months ago may no longer hold. Organizations need to continuously reassess their exposure, existing controls and the gaps that more capable AI systems could reveal.
At the same time, many organizations are relying on traditional security tools that weren’t designed to understand autonomous agent behavior.
This is one of the reasons we’re building AI Security Lab. Rather than assuming a control works because it’s configured, we’re creating practical experiments to test what agents can actually do and whether the intended security boundaries hold.
It’s an ongoing challenge, but making security more observable, testable and evidence-driven is an important part of the solution.
Significant Company Milestones
Highlighting TechRiot.io’s most significant milestones, Rajan discussed the growth of its cybersecurity podcasts, publication of his book, and launch of AI Security Lab:
One of our earliest milestones was building the Cloud Security Podcast into a platform where cybersecurity practitioners and leaders could share their experiences with a global audience. It is the #1 cloud security podcast.
Expanding into the AI Security Podcast was another important step as we saw the growing need for practical conversations about AI security. This today is the #1 AI security podcast for AI security and safety conversations with security leaders from frontier models to Fortune 500 to AI-forward companies.
Publishing AI Security Engineering with Wiley was a personal milestone, and it also helped establish the engineering-focused direction of our strategic advisory work.
More recently, launching AI Security Lab and delivering hands-on AI security education to professionals from major technology and enterprise organizations have been particularly meaningful.
What matters most to me is seeing these conversations turn into practical learning and research that security teams can apply.
What Differentiates TechRiot.io From Its Competition
When asked what distinguishes TechRiot.io from other cybersecurity research organizations and AI security providers, Rajan described its practitioner-focused approach:
There are many companies developing AI security products, and there’s important research happening across the industry but none aimed at practitioners.
Our approach is security practitioner first because we are a community of security practitioners ourselves, unlike others who have a security product to sell.
AI Security Lab is starting with questions practitioners are struggling to answer. For example, does restricting an AI agent’s permissions actually prevent it from performing an unauthorized action? How do you verify that an agent has drifted from its goal?
We use research, experiments and practitioner feedback to investigate those questions and share what we learn.
The aim is to provide independent, practical evidence that helps organizations make better security decisions, regardless of which vendors or technologies they use.
Future Company Goals
Outlining TechRiot.io’s future goals, Rajan described plans to expand AI Security Lab’s research capabilities, develop open-source tools, and provide additional hands-on cybersecurity education:
Our focus is to continue building AI Security Lab into trusted resources for people building and securing AI systems.
For AI Security Lab, that means expanding our research into agentic systems, developing practical open-source tools and creating hands-on educational experiences that help practitioners understand and test AI security controls.
I’m particularly interested in how security engineering itself will evolve as AI agents become more capable and security teams begin automating more of their workflows.
Ultimately, we want to help practitioners move from understanding AI security risks to building systems that can be secured, observed, and independently verified.